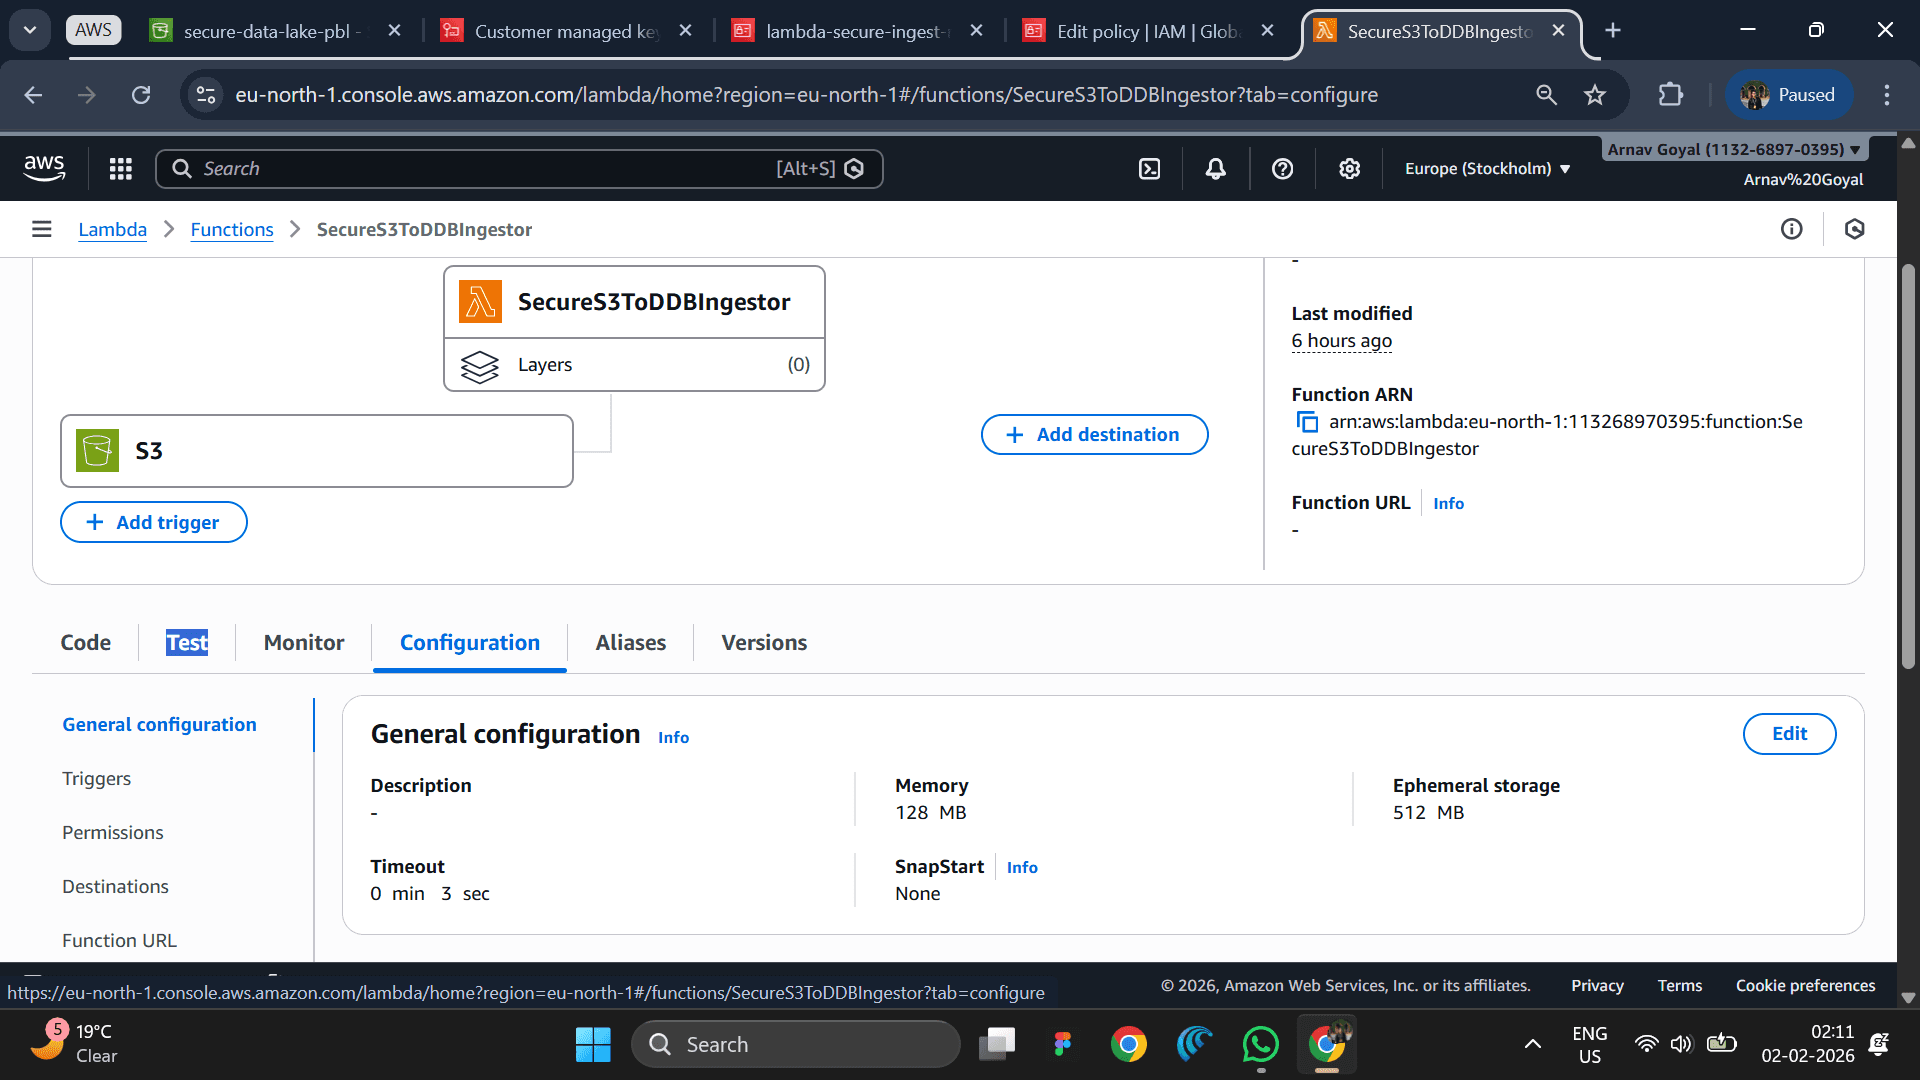
An educational serverless data ingestion architecture connecting S3, Lambda, and DynamoDB with explicit access and encryption controls.
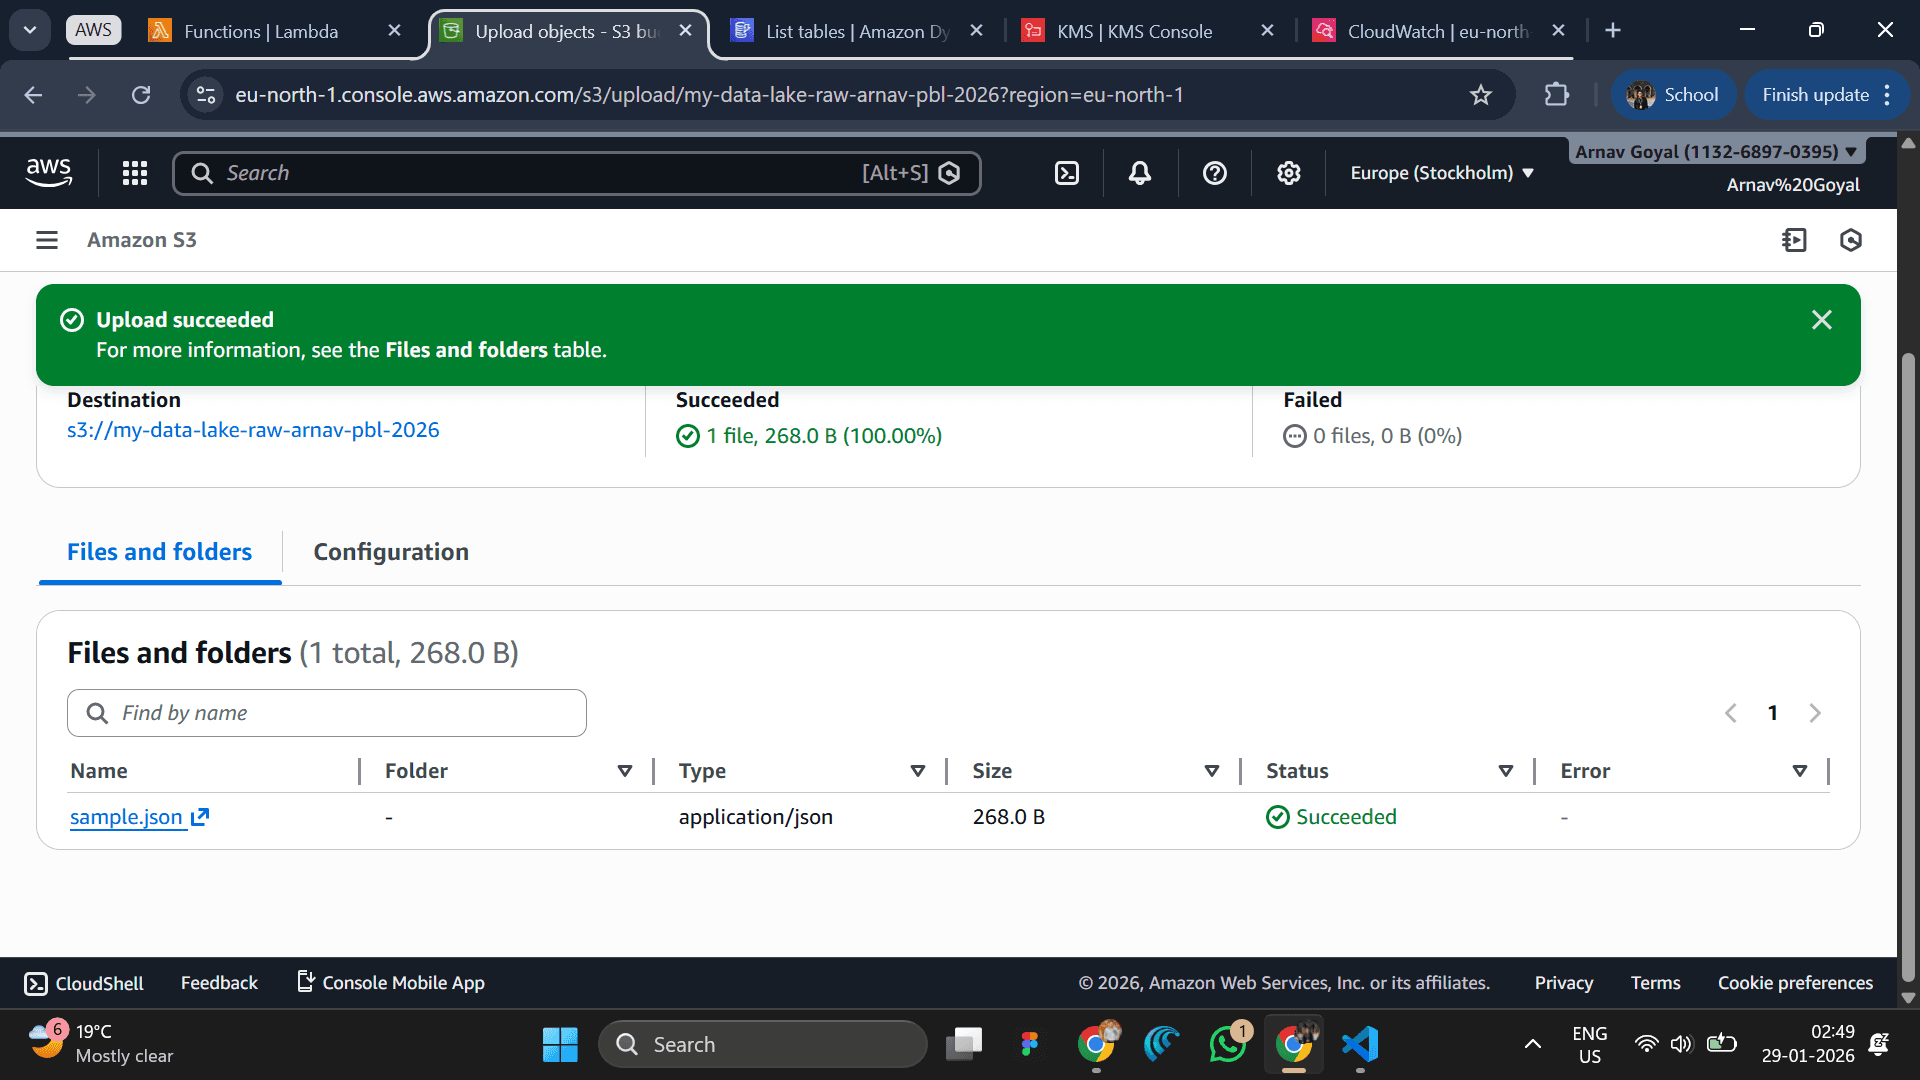
01 / 7S3 confirms a successful sample JSON upload.
Select an image to view it full size.
My contribution
Built and documented an event-driven pipeline with least-privilege roles, encryption, and audit logging.
The approach
Read a JSON array from the first S3 event record.
Keep records containing device_id, timestamp, and value, then write them to DynamoDB.
Configure HTTPS-only S3 access, scoped IAM permissions, KMS encryption, and audit logging.
Scope & perspective
The sample implements a focused ingestion path. Its field-presence check is not full schema validation, and cloud deployment and service configuration are separate from the code.